Ledger Reseller Attack Raises Questions About Hardware Wallet Supply Chains
A hardware wallet’s strongest cryptography offers little protection when an attacker can interfere with the device before its owner even switches it on. That is the uncomfortable lesson from the CryptoBilis case now facing Ledger customers in Southeast Asia.
TL;DR: Investigators have linked roughly $90 million or more in reported crypto losses to tampered wallet devices sold through a reseller channel. Ledger says its own systems were not compromised and has warned affected customers to move to newly generated recovery phrases.
The incident involves physical modifications rather than an ordinary phishing message. Reports describe implants that could capture a recovery phrase during device setup and transmit information to attackers. Once someone else possesses that phrase, they may be able to recreate the wallet without needing physical access to the device.
Ledger said confirmed cases involved wallets sold through CryptoBilis, a reseller listed in parts of Southeast Asia. It asked the reseller to stop sales and shipments while investigations continued. Customers who received affected devices were advised not to initialize them, and those already in use were told to secure funds with new credentials using trusted equipment.
The precise loss figure is still an estimate, and investigators have not publicly established a complete count of affected units. A device successfully passing an ordinary software or chip authenticity check should not automatically be interpreted as proof that no unauthorized physical component has been added elsewhere.
This attack is especially troubling because hardware wallets are bought to reduce dependence on third parties. Here, the supply chain itself became the point of exposure. For anyone buying a security device, provenance and physical integrity now deserve attention alongside firmware version and backup discipline.
Written by the News Desk and edited by Samuel Rae.
Related stories

Stablecoin Payments Reach $482 Billion As Token Supply Barely Grows
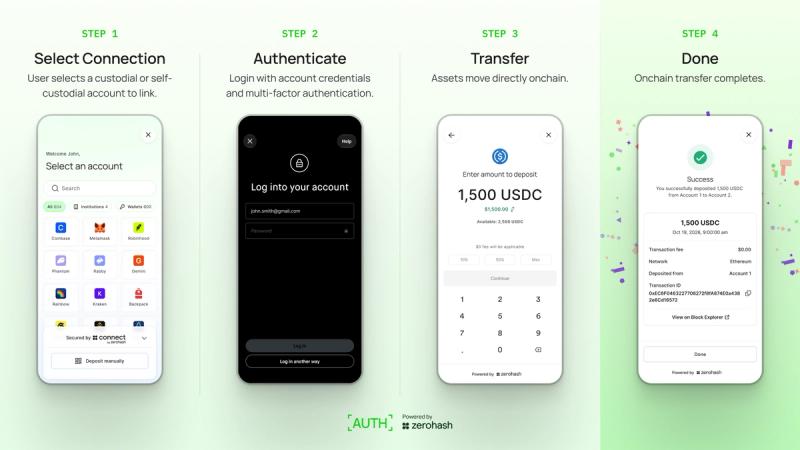
Zerohash rolls out a new tool to move crypto without copying wallet addresses
Crypto Hacks Cost $1.18 Billion In Q3 As Smart Contract Exploits Surge
